Attackers don’t break in.
They log in.

Practical writing on how account-based attacks unfold, and how to stop them.

How one stolen password becomes control of the whole network: employee, laptop, server, admin account, entire network. HasSession AdminTo MemberOf DCSync One employee clicks a fake login page Their laptop attacker signs in as them A file server an admin left a session open An admin account password copied from memory The whole network every account, every file One employeeclicks a fake login page Their laptopattacker signs in as them A file serveran admin left a session open An admin accountpassword copied from memory The whole networkevery account, every file

A common path from one stolen password to full control of a network.

Open source

I also build tools that find these paths first.

BloodHound Legacy is my fork of the attack-path mapping tool, updated to read everything modern BloodHound collects.
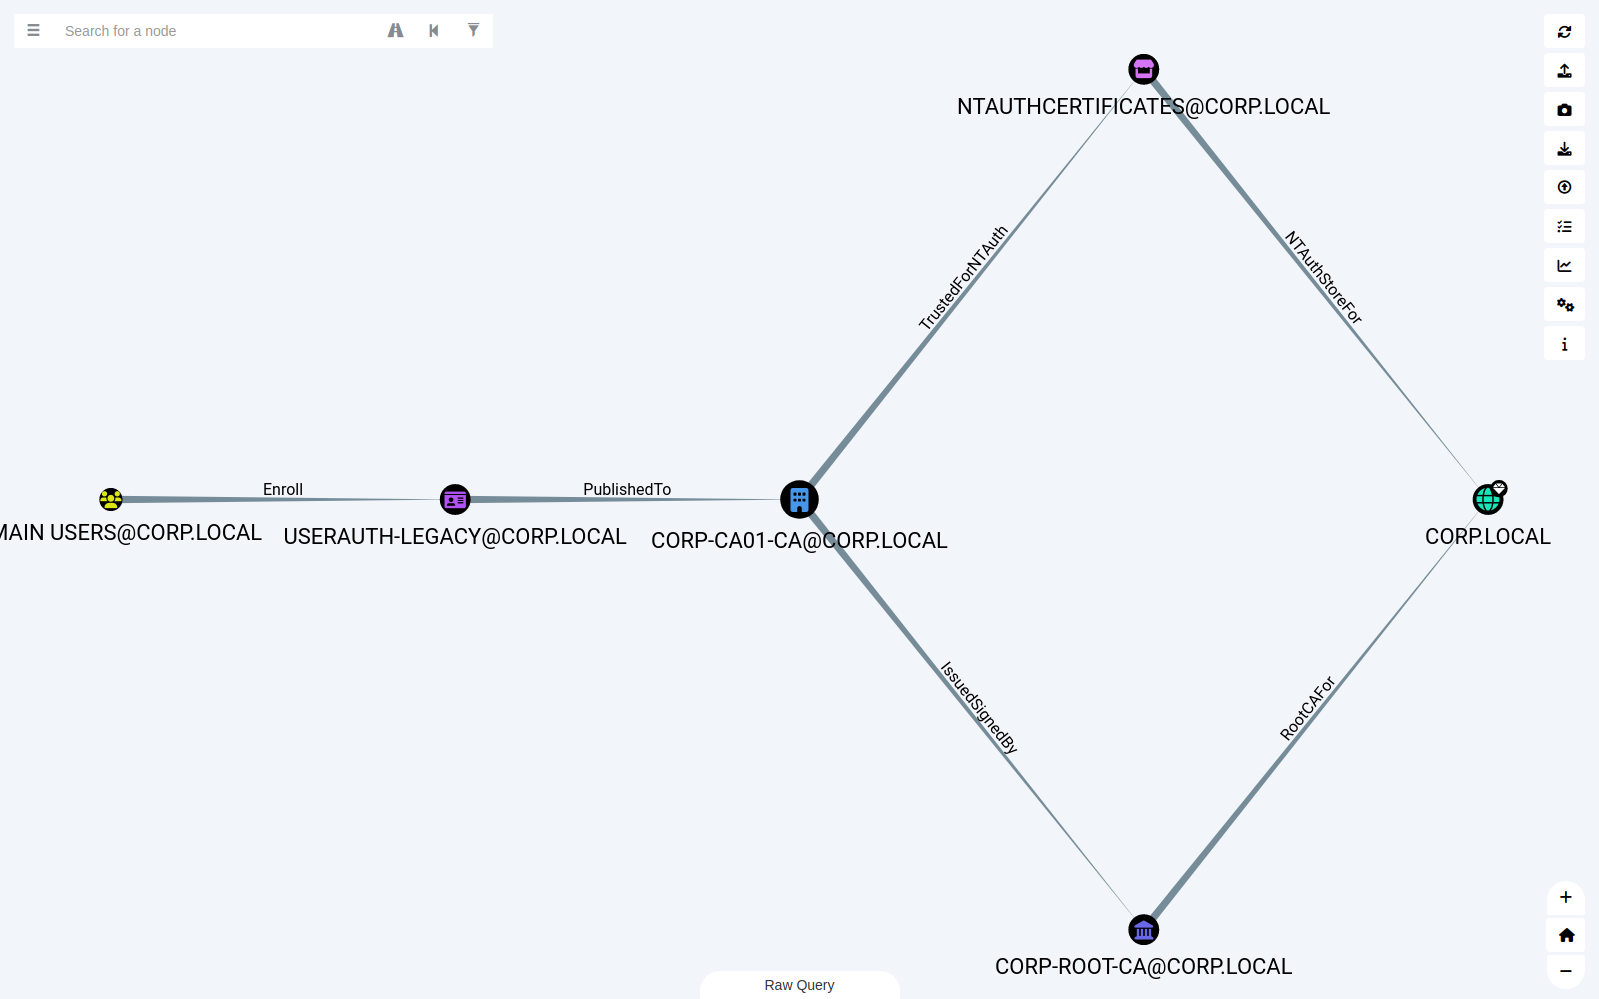
BloodHound Legacy showing an attack path in Active Directory

Latest writing

All 20 posts →
Device Code Phishing Comes for AI Coding AgentsEntra ID NTLM Signing Is Now On by Default: What Breaks in May 2027AD Hardening BloodHound Legacy 1.2 and 1.3: AD Sites and AD CS PanelsBloodHound Anatomy of a Domain CompromiseIncident Response

Ed Truderung

Incident Response Consultant

15+ years in IT. These days I focus on identity security: the logins, accounts and permissions attackers go after first.

ISC² SSCP · ISC² CC · CompTIA Security+

LinkedIn →